

Tanium tests Anthropic AI for code vulnerabilities
Wed, 16th Sep 2026 (Today)
Tanium has joined Anthropic's Project Glasswing to test Claude Mythos 5 for defensive cybersecurity work, applying the model to its own production codebase.
The effort focuses on software used by IT and security teams at thousands of organisations to manage and secure endpoint estates. Tanium plans to share its findings with the wider security community as the project develops.
The model is being used to search for vulnerabilities in the code behind Tanium's products, with the aim of identifying flaws before attackers can exploit them. The work sits within the company's internal software development and security processes rather than in customer environments.
Tanium said the initiative reflects a broader shift in software security as artificial intelligence reshapes both offence and defence. Attackers are exploiting vulnerabilities faster than many established security tools were designed to address, while newer AI systems can identify classes of risk that conventional scanning may miss.
Tanium already uses general-purpose AI models on its codebase, and participation in Project Glasswing gives it access to Anthropic's latest model for the same purpose. By testing Claude Mythos 5 against production software, the company aims to assess how frontier AI tools could change vulnerability research, triage and remediation.
The work carries added significance because of the sectors Tanium serves. Its customer base includes financial institutions, healthcare systems and government agencies, all of which depend on software security as part of their broader operational resilience.
That means flaws in vendor software can directly affect customers' security posture. For large organisations with extensive endpoint estates, visibility into software exposure and remediation speed are central concerns when assessing technology suppliers.
Code scrutiny
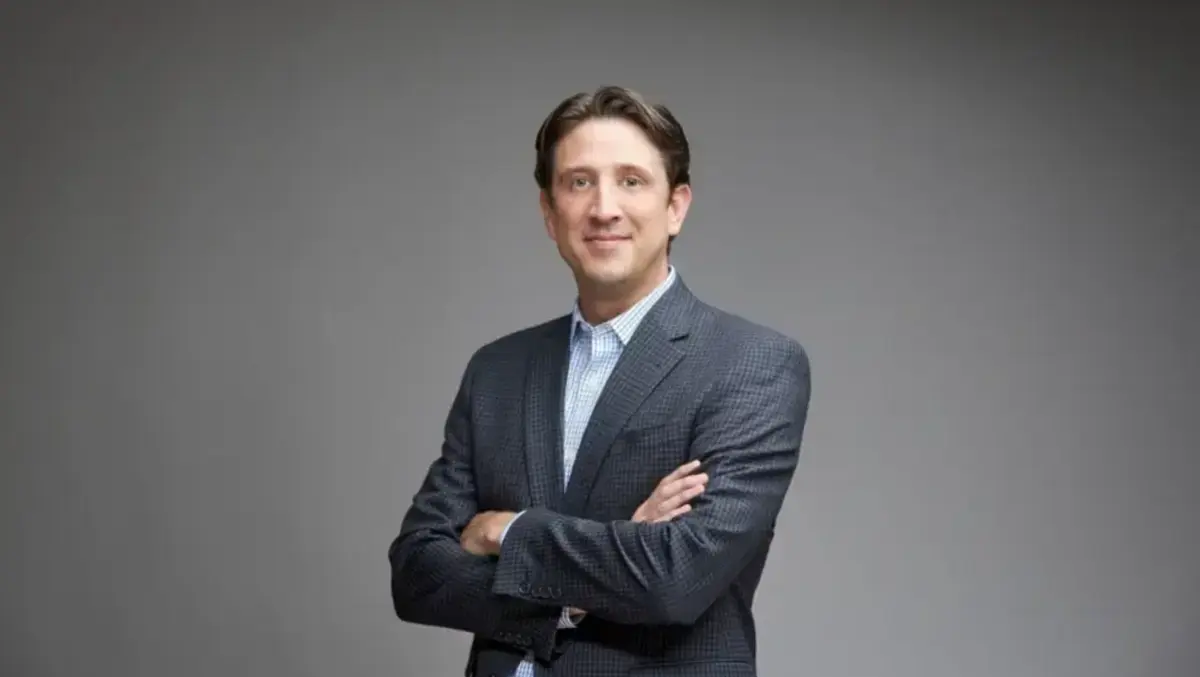
Christian Hunt, Chief Engineering Officer at Tanium, said the company views the exercise as part of its responsibility to customers.
"Every line of code Tanium ships is code that IT and security operators are trusting to protect their most critical systems," Hunt said. "Tanium takes its commitment to helping keep customers safe and secure seriously. Project Glasswing gives us access to a frontier AI capability that lets us find and fix vulnerabilities before they can be exploited and create harm for the organizations that depend on us."
Anthropic's Project Glasswing focuses on the use of advanced AI models in defensive cybersecurity settings. Tanium's participation suggests software suppliers are beginning to test whether these systems can improve code review and vulnerability discovery in production environments, rather than limiting them to research or experimental use.
One key question is whether such models can detect issues that static analysis and established scanning tools miss. Security teams have long dealt with latent weaknesses buried in mature codebases for years, becoming visible only after exploitation techniques evolve or a manual review uncovers them.
Tanium intends to publish what it learns about workflows and triage practices. That suggests the company is focusing not only on detecting software flaws, but also on the operational challenge of how security teams handle and prioritise findings generated by AI systems.
Disclosure process
Tanium also said it would continue to meet its responsibilities as a CVE Numbering Authority. That role involves publishing CVE records and security advisories for vulnerabilities affecting its products, giving customers a formal mechanism to assess exposure and plan remediation.
For enterprise and public sector users, that process remains an important part of software assurance. AI tools may help vendors find more flaws internally, but organisations still rely on clear disclosure, standardised vulnerability records and actionable guidance when deciding how urgently to patch systems.
Tanium framed transparency as a key part of its relationship with customers. In practice, that means any vulnerabilities identified in its products are expected to flow through established reporting channels, allowing security teams to compare risk, schedule remediation and document their response.
The announcement also underlines how software vendors are responding to pressure from AI-enabled threat activity. As attackers adopt more automated methods for probing code and infrastructure, suppliers face growing demands to shorten the time between vulnerability discovery and remediation in their own products.
For security buyers, the significance lies less in the use of a single model than in the emergence of new internal development practices among vendors. If AI-assisted code review becomes more effective at uncovering subtle or long-standing weaknesses, customers may begin to expect stronger evidence of how suppliers test, validate and disclose vulnerabilities in the products they deploy.
Tanium said it would publish lessons from the project on workflows, triage practices and how frontier AI is changing code security.