

DigiCert sees demand for certificate automation surge
Thu, 8th Oct 2026 (Today)
DigiCert said annual recurring revenue for its Trust Lifecycle Manager product rose 38% year on year, driven by growing enterprise demand for automated certificate management.
The update comes as organisations prepare for shorter digital certificate lifespans and broader changes in cryptography management. Public TLS certificate maximum validity is on a path to 47 days in 2029, DigiCert said, a shift that would increase renewal volumes and operational pressure for security and infrastructure teams.
Several large organisations are using Trust Lifecycle Manager, including American Red Cross, Agilent Technologies, Circle K, Hitachi, MediData, MGM Resorts International, Nokia, Schweizerische Mobiliar, and W.L. Gore & Associates. DigiCert added that some enterprise environments now exceed 100,000 certificates, making manual processes harder to sustain.
To illustrate the scale of the problem, DigiCert cited its 2026 Global PKI Research. According to the company, only 34% of organisations have a complete, current inventory of their digital certificates, while 73% are very or extremely concerned about outages caused by expired certificates.
Trust Lifecycle Manager is designed to discover certificates and cryptographic assets, centralise visibility, and automate certificate lifecycle operations across complex environments. That work is becoming more urgent as businesses try to reduce manual tasks, lower outage risk, and maintain services while certificate validity periods shrink.
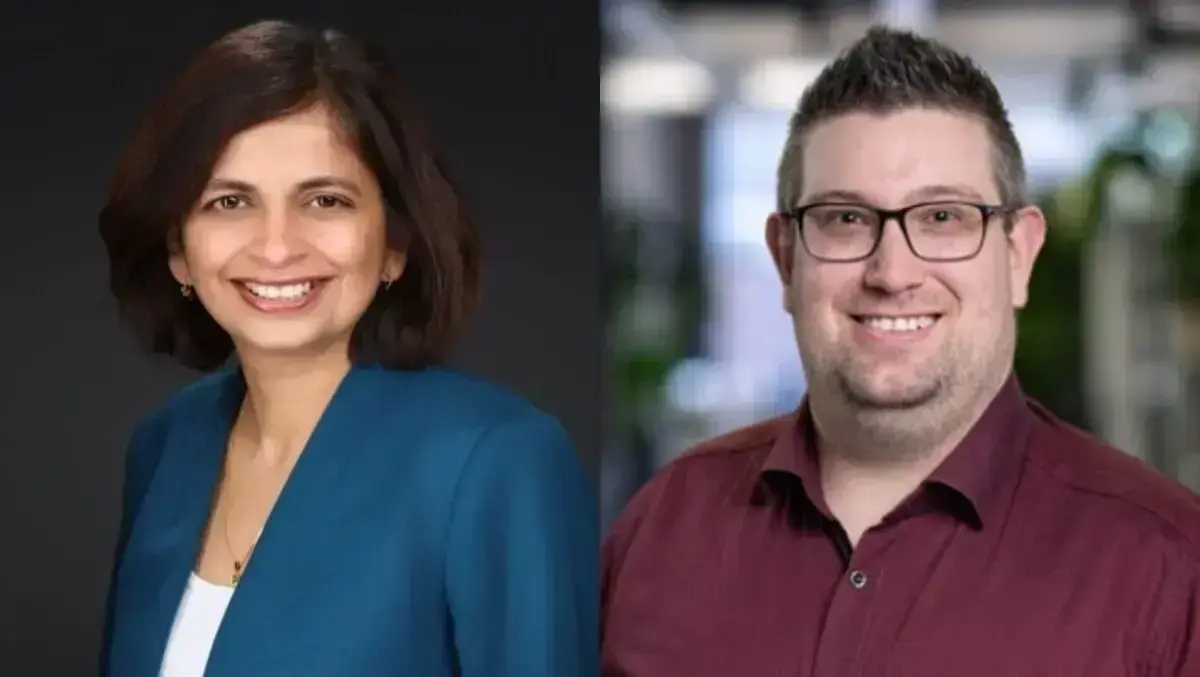
"Certificate management has become core infrastructure for the enterprise," said Deepika Chauhan, Chief Product Officer, DigiCert.
"A single missed renewal can trigger a costly outage, and shorter lifespans leave less room for error when managing thousands of certificates. The growth we're seeing in Trust Lifecycle Manager reflects customers' urgency to automate renewals, keep critical services running, and build the crypto-agility needed for the post-quantum transition," Chauhan said.
Customer demand
One customer cited by DigiCert was Schweizerische Mobiliar, the Swiss insurer, which said certificate automation is becoming more important as renewal cycles tighten.
"As certificate lifespans continue to shrink, manual certificate management becomes increasingly challenging at enterprise scale," said Kenneth Nydegger, Product Owner, Schweizerische Mobiliar.
"DigiCert Trust Lifecycle Manager provides the visibility and automation we need to manage certificates more efficiently and reduce operational risk. At the same time, it helps us prepare for future cryptographic requirements and supports a more agile and sustainable security strategy," Nydegger said.
MediData, which DigiCert described as a leading provider of secure healthcare data exchange in Switzerland, also pointed to operational scale. Its network includes 24,000 participants exchanging more than 120 million documents each year, according to DigiCert.
"Reliability is fundamental to the digital connections that support Switzerland's healthcare system," said Michael Stocker, Lead ICT-Infrastructure and ICT-Operations, MediData AG.
"With 24,000 participants exchanging more than 120 million documents through our protected digital data space each year, we need certificate management that can scale without interrupting critical workflows. DigiCert Trust Lifecycle Manager helps us automate those operations and maintain trusted connections across this ecosystem," Stocker said.
Product changes
DigiCert also outlined additions to Trust Lifecycle Manager aimed at reducing manual intervention across certificate operations. These include Continuous Validation, which uses UltraDNS to automate Domain Control Validation so domains remain validated for certificate issuance and renewal.
It has also added Apple Device Attestation to verify hardware-backed device identity before certificates are issued. Combined with an existing Jamf integration, DigiCert said the feature supports automated certificate enrolment for managed Apple devices and is intended to reduce the risk of unauthorised enrolment.
Another area of development is enterprise trust store management. DigiCert said this extends automation to root and intermediate certificates used by systems to validate trust, with centralised controls and automated distribution intended to keep trust stores consistent across corporate environments.
DigiCert is also expanding the integration ecosystem around Trust Lifecycle Manager. Named partners include BeyondTrust, F5, Fortinet, HashiCorp/IBM, HPE, Imperva, and NetScaler, which the company said would help customers connect certificate automation with the applications, infrastructure, and security products where certificates are deployed.
Market position
DigiCert said it was named a Leader in the IDC MarketScape: Worldwide Certificate Lifecycle Management 2026 Vendor Assessment. According to the company, the assessment highlighted centralised discovery, policy-based governance, and automation across public and private certificate authorities, as well as support for smaller teams handling high certificate volumes.
"Certificate lifecycle management is a strategic requirement for organisations contending with shorter certificate lifespans, rapidly expanding machine identities, and the transition to post-quantum cryptography," said Jennifer Glenn, Research Director, IDC.
"DigiCert offers capabilities required by enterprises navigating this shift. Trust Lifecycle Manager supports CA-agnostic automation, certificate discovery and governance, and operation across large, hybrid environments. These capabilities address both near-term certificate management needs and the longer-term requirement for enterprise crypto-agility," Glenn said.