

Tanium joins Microsoft AI security preview for MDASH
Fri, 16th Oct 2026 (Today)
Tanium has been selected as a testing partner for Microsoft's Codename MDASH and is taking part in a limited private preview of the security system.
The arrangement places Tanium among a small group of organisations working with Microsoft on MDASH, which uses more than 100 specialised AI agents across multiple models to identify and validate possible code vulnerabilities.
MDASH is designed to complement traditional static analysis tools by identifying issues such as logic flaws, authorisation problems, and cross-file weaknesses that rule-based methods can miss. As a testing partner, Tanium is also providing feedback on the system's development.
As part of the preview, Tanium ran the system against its own production codebase. It then paired MDASH's scanning with additional AI-assisted static and dynamic validation, followed by human review, before feeding confirmed findings into its secure development lifecycle.
The move reflects broader pressure on software and security teams to find and fix vulnerabilities before they can be exploited. As AI tools become more common in software development, companies are also facing more complex security demands around the code they produce.
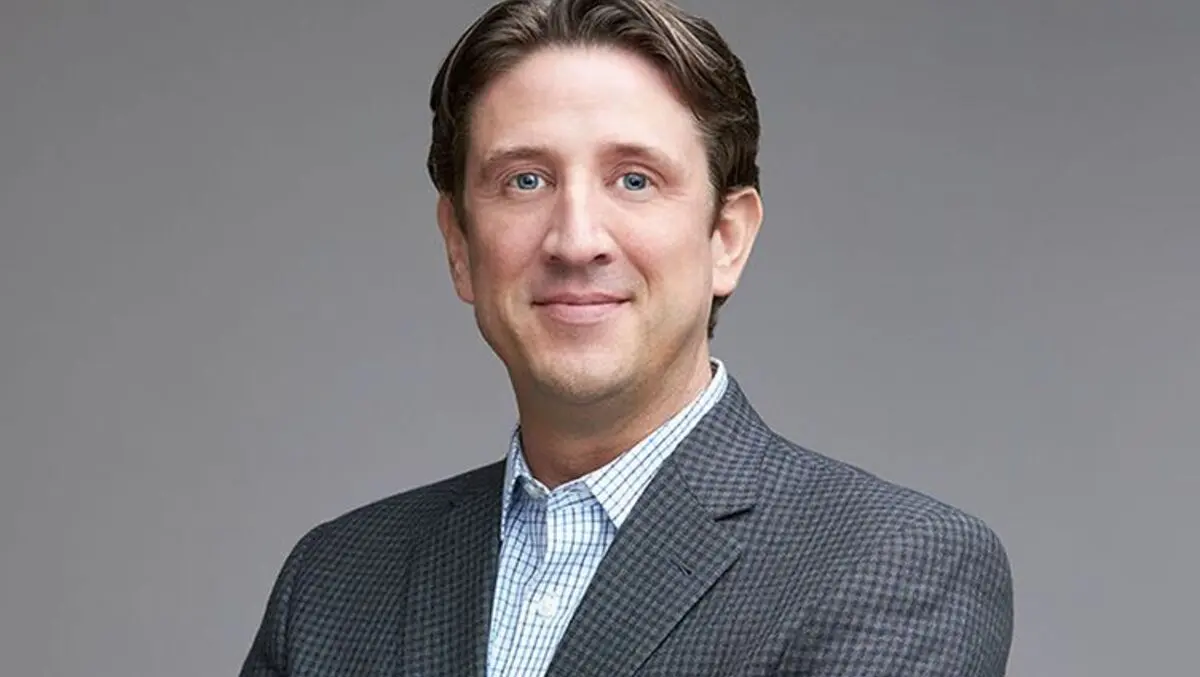
Christian Hunt, Chief of Engineering at Tanium, said the company viewed the security of its own software as central to its customer relationships.
"Our customers build their IT and security programs on Tanium, so the security of what we ship is critical for us," Hunt said.
He added that Tanium had already been using advanced AI models across its software development process.
"We quickly recognized how AI is accelerating how technology companies build and secure software and have been applying frontier model capabilities across our software development lifecycle. Being selected to test Codename MDASH lets us push these efforts further, alongside the companies defining what's possible. It's one more reflection of a commitment that has always been non-negotiable for us: earning the trust our customers place in Tanium every day," Hunt said.
Layered review
Tanium said its approach to the testing programme combines automated discovery with internal review by security engineers. It described this as a layered process in which AI surfaces potential issues at scale, while human specialists validate and prioritise the results.
That approach mirrors the "detect, decide, and remediate" framework Tanium uses in its customer products. In this case, it applied the same method to its own software development and security practices.
Loic Simon, Vice President of Security at Tanium, said the value of these tools depends on how organisations handle the findings they produce.
"The value isn't just running a scan, it's what you do with what it finds that matters," Simon said.
"We ran MDASH against Tanium code and put every meaningful finding through our own validation and remediation process. Combining agentic AI with the judgment of our security engineers is how we raise the bar on the software our customers depend on, and it's why we want to help shape tools like MDASH early," Simon said.
Security pressure
The announcement comes as software suppliers and large IT operators reassess how they manage code security in environments where both development and attack methods are increasingly shaped by AI. Vulnerability discovery tools based on machine learning have moved beyond early-stage experimentation and are now being tested in production settings.
For companies that build security and endpoint management tools, the issue carries particular weight because weaknesses in their own code can have direct consequences for customers. That has increased interest in combining automated detection systems with formal review and remediation processes rather than relying on standalone scanning tools.
Traditional static analysis remains widely used, but it has limits in detecting more complex problems spread across multiple files or linked to business logic and permissions. Systems such as MDASH are intended to broaden that search by using multiple AI models and agents to examine code in different ways.
Tanium's participation in the preview is helping inform the development of MDASH while also giving it another way to test the security of its own software.