
Hospital network blocks patient data sent to AI tools
Tue, 20th Oct 2026 (Today)
A multi-hospital healthcare network has deployed eScan Business DLP to stop patient data being shared with public AI platforms. During implementation, the system blocked hundreds of attempted transfers of sensitive information.
The network introduced endpoint-based data loss prevention controls as clinicians and administrative staff increasingly used tools such as ChatGPT, Claude and Gemini for documentation, research and routine workflows. The aim was to allow approved uses of AI while preventing protected health information from leaving the organisation's controlled environment.
eScan said the blocked or prevented transfers included patient-identifiable information, medical histories, diagnoses, laboratory results and other confidential healthcare data. These incidents were not necessarily malicious, but highlighted the risk of staff entering sensitive material into public AI services as part of their everyday work.
The controls run through an endpoint DLP agent installed on clinical workstations and administrative computers. Before data is sent to an external AI platform, the software can inspect the content, identify sensitive material, classify it, and then allow, monitor or block the transfer according to policy.
AI controls
The healthcare network also set up approved AI workflows for different tasks. General medical research queries could be directed through approved AI instances, administrative summarisation could be handled through approved internal tools, and some non-confidential queries could still be sent to public AI platforms.
The framework was backed by monitoring and audit controls to give the organisation visibility into AI-related data activity. Rather than treating all AI use as a security threat, the network created rules based on the type of work being done and the sensitivity of the information involved.
A central part of the rollout was defining what counted as sensitive data. The organisation established classifications covering patient information, personally identifiable information and other confidential clinical data, alongside policies setting out which AI platforms could be used for specific workflows.
These endpoint controls were integrated into the network's wider security and compliance framework. eScan said its software also supports audit trails, forensic logging, risk identification and reporting for compliance reviews and internal investigations.
Broader issue
The case reflects a wider issue facing hospitals and health systems as generative AI tools become embedded in daily operations. Staff may use large language models to draft discharge summaries, support medical research, assist with administrative tasks or prepare documents, but in doing so they can expose protected information to systems outside the employer's direct control.
Healthcare organisations face a particular challenge because patient names, records, diagnoses, clinical histories and test results are among the most sensitive categories of data they hold. Once entered into a public AI tool, that information may move beyond the hospital or network's security boundary, creating privacy, governance and compliance risks.
eScan said its DLP software is designed to address those risks through content-aware inspection, automated classification and controls tied to data movement. Beyond AI platforms, the product also monitors other transfer channels, including email, file transfers and external storage devices.
Clinician adoption was another part of the implementation. Early use by clinical champions helped build wider acceptance across teams, while the combination of monitoring and policy controls was positioned as a way to support existing workflows rather than halt AI use altogether.
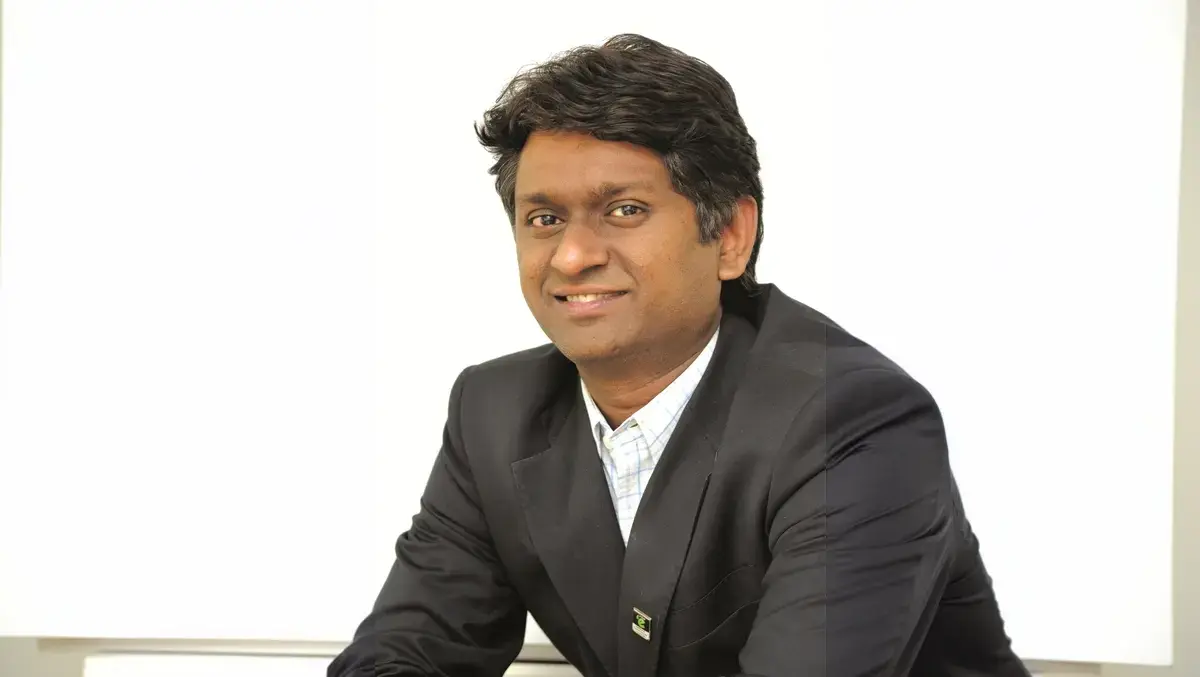
Govind Rammurthy, Chief Executive Officer and Managing Director at eScan, said: "Healthcare organisations are caught between two genuine pressures: enable innovation and protect patient privacy. Both matter. The solution is monitoring - knowing what data staff are sending to AI models hosted on the internet, automatically blocking sensitive information while allowing legitimate queries. It requires visibility into data movement and the ability to enforce policies at the endpoint level. You don't need to restrict innovation. You need to control data flow."