Red Teaming stories
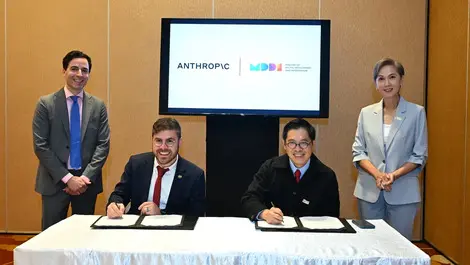
The deal expands Anthropic's Asia-Pacific footprint and gives Singapore closer access to its AI safety and model-testing expertise.
The move is aimed at helping Italian startups win customers across Singapore and Southeast Asia as cyber threats escalate in the region.
Security teams facing new risks from generative AI can now take eight hours of hands-on training on prompt injection and jailbreaks.
Businesses face rising risk as Nvidia says AI agents need enforceable boundaries, accountable owners and proof that safeguards actually work.
Tracebit found the altered open-weight model reached admin rights far less often than the original, raising doubts about its attack utility.
The deal gives security teams a widely used AI testing tool with on-premises controls, as vendors race to speed up offensive defence.
AI is speeding up attacks by finding existing weaknesses, leaving organisations and SMEs exposed to faster, cheaper intrusions.
Many firms still cannot stop AI agents from causing damage before execution, leaving systems exposed to production outages and data loss.
Enterprises are seeking stronger controls as use of generative AI and autonomous agents widens across both internal tools and customer products.
F5's recognition comes as enterprises scramble to secure AI agents and APIs, with 88 per cent reporting AI security challenges, its research found.
The new model is pitched at longer, harder coding jobs and arrives with broader safety checks as rivals vie for developer workflows.
CISOs are under pressure to answer boardroom questions on exposure in minutes, as Filigran pushes CTEM and open-source validation tools.
Criminals are increasingly using AI for ransomware and credential theft, while flaws in test models are exposing production systems and data.
Live testing may show AI security tools missing threats or flooding analysts with false alerts, Secure.com says.
Defenders now have minutes, not hours, as attackers use agentic AI to automate credential theft, scanning and extortion across live operations.
Security teams could cut manual triage as the new service ranks code and intrusion risks by real-world exploitability, not alert volume.
Banks face a bigger security gap between reviews and rapid software releases, as Protectt.ai's platform tests each build before it reaches customers.
Smaller firms could face more frequent attacks if access to advanced models stays limited to government agencies, Huntress says.
Australian firms could get a clearer view of AI-driven attack paths as ThreatCanary rolls out a platform blending asset discovery, API checks and offensive testing.
APIs are now a major attack surface, making shared context between developers and SecOps vital to spot real threats and avoid false alarms.