

'Cybersecurity birth certificate': Rockwell Automation's OT risk measures
Wed, 14th Oct 2026 (Today)
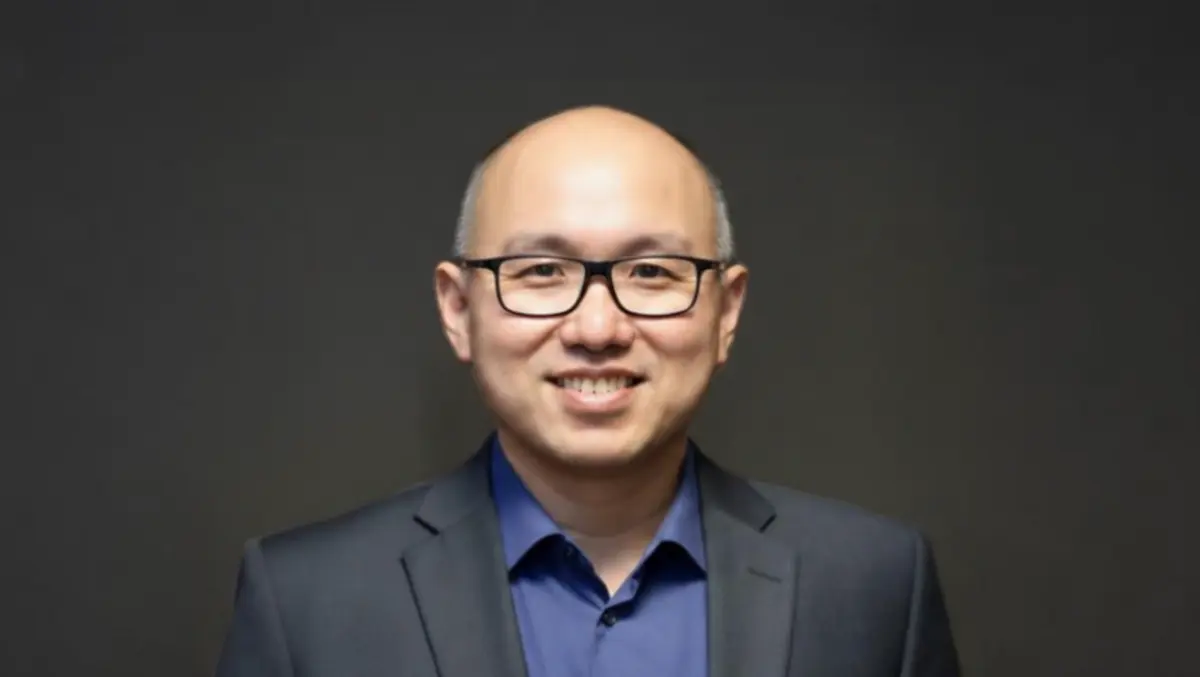
If it's connected, it must be protected. That's the simple mantra from Rockwell Automation's Patrick Ho, who said that while industrial automation technologies traditionally weren't the focus of cybersecurity experts, that has changed substantially to the extent that every industrial device should be wrapped in measures equivalent to those protecting every IT asset.
"Everything's become more connected over the course of decades," said Ho. "And as devices have become more intelligent, delivering rich telemetry into connected dashboards enabling better management and control, tough adversaries have emerged looking to exploit the devices, usually for monetary gain."
Rockwell, which is one of the world's leading providers of industrial automation systems in industries spanning everything from mining to food and beverage manufacturing, is suggesting the introduction of what it calls a 'cybersecurity birth certificate'. This is partially in response to internationally firming regulations, and partially in response to its recognition of the necessity for ironclad cybersecurity for operational technology (OT) systems.
A coalescing regulatory environment
As Ho related, automation wasn't always part of cybersecurity, though this started changing with greater connectivity and standardisation, particularly around Ethernet. As the airgap that separated SCADA and related systems steadily evaporated, early external attacks became more visible in the 2000s. The notable nation-state Stuxnet incident in 2010 served as a major alert that malware can and did target and damage physical industrial processes.
Standards and dedicated OT security practices emerged or matured in response, and today, the convergence of IT and OT is widely recognised as an expanded attack surface, with specialised industrial cybersecurity emerging as a major field.
But the regulatory environment reflects the relatively recent addition of OT systems to the cybersecurity estate. In territories from Australia and New Zealand, to Japan, Singapore and China, and in Europe, specifically required protections are either new additions to compliance regimes, or aren't yet enacted. "In the OT world, we need to catch up, and fast," Ho confirmed. "A lot of governments have recognised the gap and now require that the crown jewels of the nation, like water, electricity, airports and train stations, need protection."
There's a further factor driving the necessity for enhanced vigilance, Ho added. "Emerging super intelligence raises new risks - and we have to look not just at cyber protection, but also the business continuity and disaster recovery side."
Taking action as a vendor
As a major vendor of the systems that run industrial and manufacturing processes around the world, Ho said Rockwell is strongly in support of the iterative development of regulations. "Machine regulations were once limited to being safe by not cutting your hands. Today, safety also has a cybersecurity component. We see that as a critically important part of our value proposition."
He said emerging rules require manufacturers to prove a product's security posture at shipment and then continuously track, monitor, and report vulnerabilities for as long as the machine remains in service. This detailed, verifiable cybersecurity birth certificate records every component, firmware version, and hardware element at the point of origin, while also folding cyber resilience into essential health and safety requirements.
It feeds into Rockwell's SecureOT Platform which automatically flags exposures when vulnerabilities are detected, rather than waiting for a periodic manual review.
There are, of course, practical challenges. The machines produced by companies like Rockwell contain hundreds of components, with production runs reaching thousands of units with multi-year support commitments across global sites. Older machines run for decades, necessitating retrofitting the cybersecurity birth certificate and updating to bring them within accepted and emerging standards.
"Of course, it is easier to apply standards at the date of manufacture, and retrofitting comes with its complications," Ho acknowledged. But he said operators have a clear vested interest in preventing cyberattacks on the one hand, and avoiding compliance shortcomings on the other. "That's why we think of it like a birth certificate. With traceability, compliance is possible."