

AI agents now seen as biggest insider risk, Exabeam
Thu, 17th Sep 2026 (Today)
Exabeam has published research showing that security leaders now rank AI agents with excessive, compromised or unintended access as the biggest threat to their organisations. The survey covered 600 security and finance decision-makers across seven countries.
Nearly half of security leaders, 48%, placed AI agents ahead of external threat actors, compromised insiders and malicious insiders as the top current risk to their organisation. External threat actors were cited by 28% of respondents, while compromised insiders and malicious insiders were each named by 12%.
The findings suggest a shift in how companies define insider risk as more autonomous software systems gain access to internal resources and take actions with limited human oversight. In the research, AI agents were defined as goal-driven autonomous systems rather than conversational chatbots.
Security teams are already expanding how they monitor these systems. The survey found that 60% of respondents use dedicated AI security or governance tools, 56% extend existing SIEM, detection or monitoring platforms, and another 56% use behavioural monitoring and baselining. A further 29% still rely on manual review.
Yet broader monitoring has not closed significant gaps. More than a quarter, 27%, said limited behavioural context and correlation was the biggest weakness in their current approach. Poor visibility across environments, alert prioritisation and manual processes were also cited as ongoing problems.
Behaviour gaps
The results suggest many organisations can see individual actions by AI agents but still struggle to understand how those actions connect across systems and over time. That matters because an agent may appear to operate normally in one application while its wider pattern of behaviour points to misuse, compromise or activity outside its intended permissions.
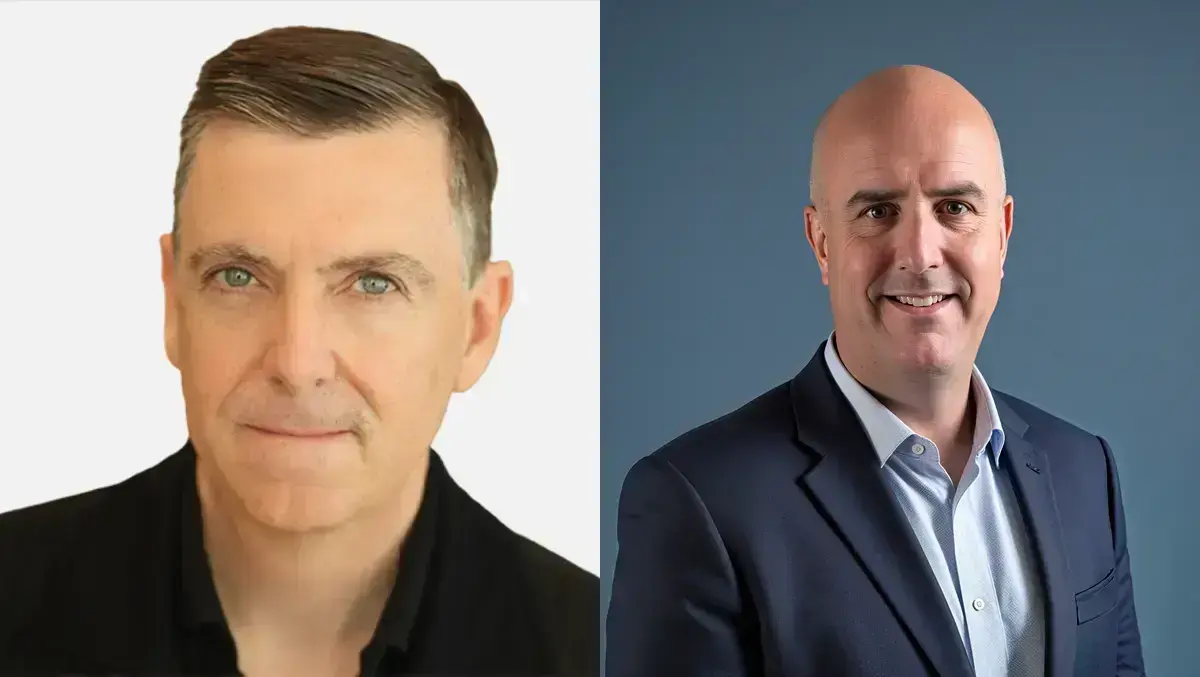
Steve Wilson, Chief AI and Product Officer at Exabeam, said the distinction between observing activity and understanding intent had become central to security operations.
"Organisations are making meaningful progress in monitoring AI agents, but monitoring activity isn't the same as understanding behaviour," said Steve Wilson, Chief AI and Product Officer at Exabeam. "AI agents operate with legitimate access and interact across multiple systems, making individual actions appear routine. Security teams need the context to connect those actions over time so they can distinguish expected automation from misuse, compromise or unintended behaviour."
The study also found broad concern over access to sensitive data, actions beyond intended permissions, the complexity of investigations, and limited visibility into AI agent behaviour. Those concerns were shared by both security and finance leaders, suggesting the issue is no longer confined to technical teams.
Budget pressure
On cyber risk tolerance, security and finance leaders appeared closely aligned. The survey found that 93% said the two functions agree on cybersecurity risk tolerance, while 81% of security leaders said their Chief Financial Officer understands the cyber risks they are trying to mitigate.
Even so, support in principle does not always lead to funding. More than half of security leaders, 55%, said they had delayed or scaled back a security initiative because they could not frame the risk in financial terms their Chief Financial Officer would accept.
That points to a persistent issue for cyber teams: translating technical threats into business impact in a way that supports investment decisions. Finance leaders may accept that a risk exists, but still require a clearer view of how proposed spending would change the company's exposure.
Mike Byron, Chief Financial Officer at Exabeam, said the challenge was less about proving cyber threats exist than quantifying the benefit of spending to address them.
"CFOs rarely question whether a cybersecurity risk is real," said Mike Byron, Chief Financial Officer at Exabeam. "The challenge is understanding how a proposed investment reduces that risk in measurable business terms. When security teams connect technical outcomes to business impact, investment decisions become much easier."
The survey was conducted among organisations with 500 or more employees in the United States, Canada, the United Kingdom, France, Germany, the Netherlands and Australia. Half of respondents were IT decision-makers responsible for security, and half were finance decision-makers.
The findings show companies are watching AI agents more closely while still lacking a complete view of what those agents are doing across business systems. At the same time, security teams face pressure to justify spending in language finance leaders can tie directly to business risk.